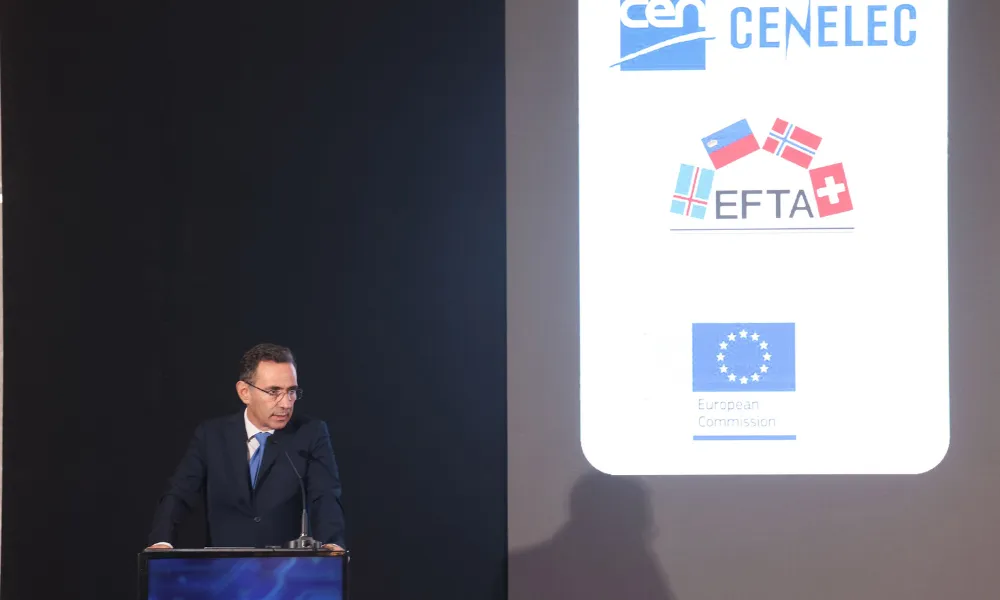
Manufacturers of digital products must now report actively exploited vulnerabilities and severe security incidents under new European Union rules that came into force earlier this month, Deputy Minister of Research, Innovation and Digital Policy Nicodemos Damianou said on Monday.
Speaking at a conference in Nicosia titled "Building CRA compliance through horizontal cybersecurity standards,"Mr Damianou said the broader goal facing the sector is to "build products people can trust" from a cybersecurity standpoint.
First obligations under the Cyber Resilience Act take effect
Mr Damianou said that as of 11 September, the first obligations under the Cyber Resilience Act (CRA) came into force, requiring manufacturers to report actively exploited vulnerabilities and severe incidents through reporting arrangements run by the European Union Agency for Cybersecurity (ENISA). He noted that the CRA's full set of essential requirements will eventually apply to every product containing digital elements sold on the European market.
New standards aim to simplify compliance
Under a standardisation request from the European Commission, three European standards bodies, the European Committee for Standardisation (CEN), the European Committee for Electrotechnical Standardisation (CENELEC) and the European Telecommunications Standards Institute (ETSI), are developing harmonised standards to support the CRA's implementation, covering areas such as secure design and vulnerability handling that apply across all products regardless of type.
"These standards give manufacturers something enormously valuable: one clear, recognised route to compliance, instead of twenty-seven interpretations of the same article," Mr Damianou said.
Cyprus's role during its EU Council presidency
Mr Damianou pointed to Cyprus's recent Presidency of the Council of the European Union, which ran until June, saying he had told fellow ministers in Brussels before it began that cyber resilience would be one of Cyprus's three digital priorities. "Sovereignty and autonomy are not about isolation," he said.
During the presidency, Cyprus worked on a revision of the Cybersecurity Act, aimed at strengthening ENISA and simplifying certification, and brought the revision before the Telecom Council in June. Cyprus also hosted Europe's cybersecurity certification community during this period. Mr Damianou added that the Digital Omnibus, which proposes a single entry point for incident reporting, is now being handled by the Irish Presidency, which took over from Cyprus.
Mr Damianou said Europe "cannot afford to be merely a regulator of technologies developed elsewhere."
Cyprus's national preparations
On measures taken domestically, Mr Damianou said the Digital Security Authority is central to Cyprus's preparations for the CRA. He added that the Council of Ministers approved a unified Cybersecurity Policy Framework for government and the wider public sector for the first time this summer.
Concerns for smaller Cypriot businesses
Addressing the impact on Cypriot small and medium-sized enterprises (SMEs), Mr Damianou said most Cypriot manufacturers and software developers lack a dedicated compliance department. "For them, a practical, accessible standard is the difference between compliance as a burden and compliance as a competitive advantage," he said.
He also framed the CRA as more than a security measure, describing it as "also a Single Market measure," and said a company that builds secure products once should be able to place them across the European market with confidence.
"The huge task at hand is at the end of the day to build products people can trust from a cybersecurity perspective," Mr Damianou concluded.